A firewall should protect your network without becoming the reason your printer disappears, a payment terminal stops working, or remote employees cannot sign in. Knowing how to set up firewall protection starts with one simple goal: allow the traffic your home or business actually needs, and block everything else.
For most Salt Lake City homeowners, remote workers, and small businesses, the safest setup is not the most complicated one. It is the one you understand, keep updated, and test before relying on it.
Start by identifying which firewall you already have
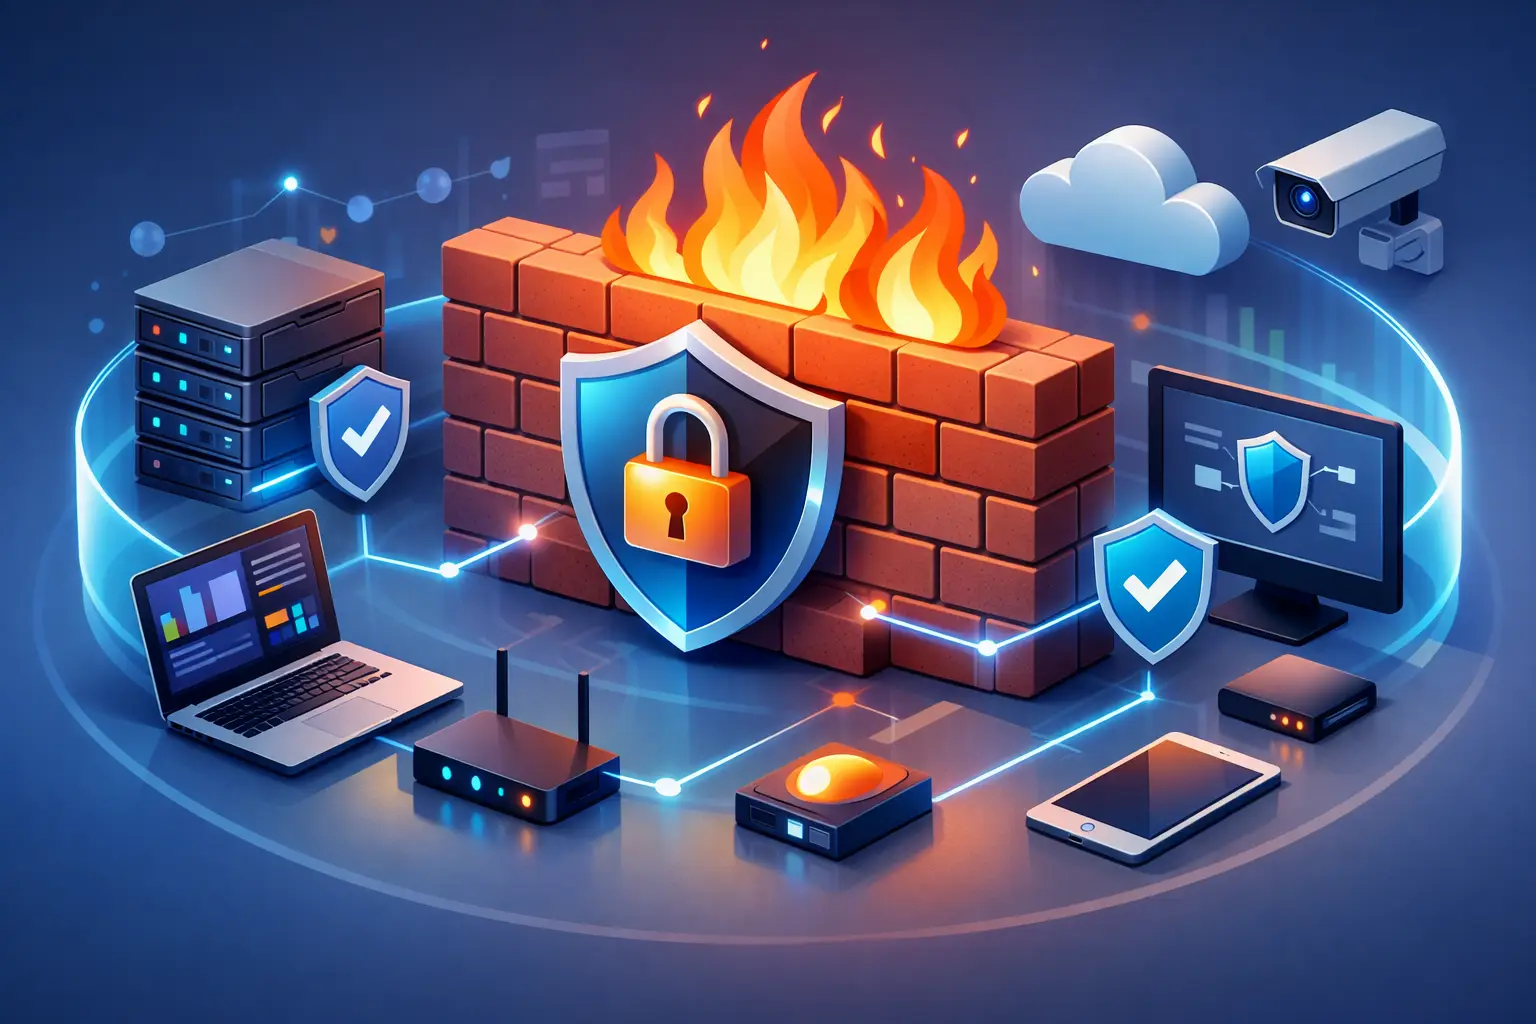
Many people have more firewall protection than they realize. A typical home or small office may have a firewall built into the internet router, another one enabled on each Windows or Mac computer, and security software with its own network controls. These layers can work together, but conflicting settings can also cause connection problems.
Your router firewall protects the entire network from unwanted traffic coming in from the internet. Your computer firewall controls which apps and services can communicate with that individual device. Both matter. The router is your front door; the device firewall helps keep an issue on one computer from spreading further.
Before changing settings, write down what is connected to the network. Include computers, phones, printers, smart TVs, security cameras, file servers, point-of-sale equipment, and any remote-access tools. A small business should also note cloud applications, VPN access, shared folders, and devices used by employees working from home.
This quick inventory prevents a common mistake: blocking a service because nobody realized it was necessary.
How to set up firewall protection step by step
Secure the router first
Sign in to your router or firewall appliance using its management address. This is usually done from a computer already connected to your network. If you do not know the address or login, check the router label, your internet provider documentation, or the device settings.
Change the default administrator password immediately if it is still in place. Use a long, unique password stored in a password manager. Also check that the router’s management page cannot be accessed from the internet. Remote administration should be disabled unless there is a specific business need for it and it is protected by a VPN and strong multi-factor authentication.
Next, turn on automatic firmware updates if the device supports them. Router updates often fix security flaws that attackers actively look for. An old router with no current updates may still provide basic connectivity, but it is not a good long-term security choice.
For most homes, the firewall setting should remain enabled at its default level. Avoid opening ports just to make a warning message go away. Port forwarding creates a path from the public internet to a device on your network. It can be needed for a carefully planned service, but it should never be a casual troubleshooting step.
Keep device firewalls enabled
On Windows, confirm that Microsoft Defender Firewall is turned on for private and public networks. On a Mac, check that the built-in firewall is enabled in system settings. These default firewalls are appropriate for most people and usually require little maintenance.
When an application asks for firewall permission, pause before clicking Allow. Verify that you recognize the program and consider which network you are on. A trusted printer utility may need access on your private home or office network. The same permission on a public Wi-Fi network may be unnecessary.
Do not disable a device firewall permanently because one program cannot connect. Instead, identify the program, remove old or duplicate rules, and create the narrowest rule that solves the issue. Allowing one approved app is far safer than allowing all incoming connections.
Use network profiles correctly
Windows and other operating systems treat trusted private networks differently from public ones. Your home or office network should generally be marked Private only if you control it and it is protected with a strong Wi-Fi password. Coffee shop, hotel, airport, and guest Wi-Fi networks should always be Public.
The difference is meaningful. Public profiles limit device discovery and sharing, making it harder for other people on the same network to find your computer. If file sharing, printer sharing, or network discovery is needed at an office, allow it only on the private business network.
Separate devices that do not need access to your work systems
A guest Wi-Fi network is one of the easiest firewall-adjacent improvements you can make. Put visitors, personal phones, smart speakers, TVs, and other internet-connected devices on a separate guest or Internet of Things network when your router supports it.
For a small business, separation is even more valuable. Employee workstations, guest Wi-Fi, payment systems, cameras, and servers should not all sit on one open network. Proper network segmentation limits the damage if a weak device is compromised. It does require planning, though, because some devices need to communicate across segments. Printers, cameras, and phone systems are frequent examples.
Rules to avoid creating an accidental security gap
Firewall rules should be specific. A rule that permits one application to reach one destination or service is easier to review than a broad rule allowing every device and every port.
Be particularly cautious with remote desktop access. Exposing Remote Desktop Protocol directly to the internet is a common source of attacks against small businesses. If staff need remote access, a properly configured VPN, multi-factor authentication, limited user permissions, and monitored access are safer choices. The right setup depends on the number of users, the applications they need, and whether a server or cloud service is involved.
You should also remove rules you no longer need. Old rules often remain after an employee leaves, a computer is replaced, or a temporary vendor project ends. Review firewall rules at least a few times a year and after any major network change.
A useful rule of thumb is this: block unsolicited inbound traffic by default, allow normal outbound web access, and add exceptions only when there is a documented reason. More restrictive outbound controls can help a business, but they need testing. If they are too aggressive, software updates, cloud backups, video meetings, and line-of-business applications can fail.
Test the setup before calling it finished
A firewall configuration is not complete until it is tested. Start with daily tasks: browse the web, send email, print a document, access shared files, run a video call, and use any business-critical software. If your business uses a VPN, test it from outside the office network as well.
Then confirm that the protections are still active. Check that the router firewall and device firewalls are enabled, that no unknown port-forwarding rules exist, and that the administrator account uses a strong password. Save a copy or screenshot of the configuration before making major changes, especially on a business firewall appliance.
If something stops working, do not turn off the firewall as a permanent fix. Check the firewall logs to see what traffic was blocked and when. The log can point to the device, application, port, or rule involved. From there, add a precise exception or correct a network setting.
When a home setup becomes a business IT project
A basic router firewall is often enough for a household with current devices, secure Wi-Fi, and no exposed services. A business may need more: separate networks, VPN access, content filtering, intrusion detection, centralized logging, backup internet, and rules for servers or specialized applications.
That does not mean every small company needs an expensive enterprise firewall. The right equipment and configuration depend on your number of users, remote-access needs, customer data, compliance obligations, and tolerance for downtime. A five-person office with cloud software has different needs than a clinic, retailer, law office, or company running an on-site server.
If you are unsure which rule is safe to change, getting help before opening a port is usually faster and less stressful than recovering after an exposure or outage. Don’t Panic! Computer Repair can assess a home or small business network on-site, explain the options clearly, and help set up security without leaving your team disconnected. A few careful settings now can save a great deal of disruption later.